KYC & onboarding
ID document and selfie checks, sanctions and PEP screening, and risk-based approval in minutes.
Digital banking, payments and lending products built compliance-first. We scope the regulatory perimeter before writing code, because that is what decides your architecture.
Trusted by teams worldwide
Fintech app development is building software that moves, stores or manages money for customers: digital banks, wallets, payment apps, lending, investing and insurance products. Beyond the app screens it covers identity checks (KYC), anti-money-laundering monitoring, a ledger that always balances, secure payment integrations and the rules of every market you operate in.
Appther builds fintech apps end to end, from compliance scoping and architecture to iOS, Android, web and the back office your operations team runs on. Every project starts with a fixed-price proposal, so the budget is agreed before the build.
Updated · Reviewed by Appther’s fintech engineering team
Six product categories covering the regulated financial services we build most often.
Most financial products are assembled from the same twelve building blocks. Your scope decides which ones are built, which are bought from a provider and which can wait for version two.
ID document and selfie checks, sanctions and PEP screening, and risk-based approval in minutes.
A double-entry ledger that reconciles every balance, fee and reversal to the cent.
Virtual and physical cards through issuers such as Marqeta, with spend controls and instant freeze.
P2P, ACH, SEPA, UPI and cross-border rails with status tracking the user can understand.
Account linking and data aggregation through Plaid, TrueLayer or a regulated provider in your market.
Rules plus machine learning on device, behaviour and transaction signals, with case review for analysts.
Applications, credit decisioning, repayment schedules, collections and key-fact disclosures.
Brokerage and custody integrations, model portfolios, rebalancing and tax documents.
Real-time alerts, monthly statements and receipts, delivered in-app, by email and SMS.
Guided dispute flows, evidence collection and timelines that match card-network rules.
Customer search, limits, manual reviews, suspicious activity cases and role-based access.
Regulatory reports, reconciliations and an immutable log of who changed what and when.
The parts that decide whether you pass diligence, backed by our API and data teams.
Multi-currency remittance and international transfer apps with FX, compliance screening, and low-cost payout rails.
Crypto wallets, exchanges, DeFi, and tokenization platforms with secure key management and on/off-ramp integrations.
Automated KYC/AML, transaction monitoring, fraud analytics, and regulatory reporting tools that keep you audit-ready.
We map your business model, target markets, and the exact regulatory requirements, defining the compliance and security blueprint before a line of cod
Clickable prototypes plus a scalable, zero-trust system design covering data flows, integrations, and infrastructure.
Two-week sprints with a working prototype by week 3, so you validate features early and steer the build with confidence.
The rules change by country, and so does the architecture. These are the frameworks we scope most often and what each one changes in the build.
| Market | Main rules | What it changes in the build |
|---|---|---|
| United States | PCI DSS v4.0, the GLBA Safeguards Rule, Bank Secrecy Act AML with FinCEN, and state money transmitter licences | Card data tokenised out of your systems, sanctions and transaction monitoring, and a sponsor-bank or licensed-partner model |
| United Kingdom | FCA authorisation or an agent model, the Payment Services Regulations with Strong Customer Authentication, Consumer Duty and Open Banking | SCA journeys with biometrics, plain-language disclosures with outcome monitoring, and Open Banking through a regulated provider |
| European Union | PSD2, DORA for ICT resilience, GDPR, AML directives and MiCA for crypto-assets | Consent and SCA flows, incident reporting and third-party risk registers, data residency and erasure requests |
| Canada | FINTRAC AML reporting, Retail Payment Activities Act registration with the Bank of Canada, PIPEDA and Quebec Law 25 | Suspicious and large-transaction reporting, safeguarding of client funds and privacy impact assessments |
| Australia | ASIC licensing, AUSTRAC AML/CTF rules, the Consumer Data Right and the Privacy Act | Ongoing customer due diligence, CDR accreditation or an accredited intermediary, and breach notification |
| India | RBI rules for payment aggregators, prepaid instruments and digital lending, NPCI rules for UPI, and the DPDP Act | Payment data stored in India, UPI through a sponsor bank or PSP, and key fact statements with direct loan disbursal |
| Nigeria | CBN licence categories, BVN and NIN identity checks, and the Nigeria Data Protection Act | Identity checks at onboarding, NIBSS and switch integrations, and local data handling |
| UAE | CBUAE rules for stored value and retail payments, VARA or ADGM and DIFC rules for virtual assets, and the UAE PDPL | UAE Pass identity, Arabic and English interfaces, and hosting that meets the regulator’s expectations |
Licences belong to your company or your partner bank. We build the software to meet the obligations, and your compliance counsel signs off the scope. Market guides: Nigeria and Ethiopia.
One call about your product, your markets and who holds the money tells you which licences and controls apply, what that means for your architecture and a fixed budget.
Get Your Free AuditFree · No obligation · Delivered within 48 hours
A process where the regulatory perimeter is settled before architecture, not discovered during audit.
We map the product, markets, money flow and regulatory perimeter, then agree a fixed quote.
Secure architecture, data residency and KYC/AML flows designed before build.
Product built in sprints with security review at every milestone.
Penetration testing, load testing and a compliance readiness review.
Launch with monitoring, fraud alerting and ongoing support.
Card data handling scoped out of your estate wherever possible.
Identity and screening flows designed with the product.
What a payments backend has to hold to keep money moving.
Typical time from discovery to a live, compliant product.
Most fintech apps fall into one of three bands. Compliance and integrations, not screens, decide where yours lands.
| Stage | What you get | Timeline | Typical budget (USD) |
|---|---|---|---|
| MVP | One core flow, such as a wallet, payments or lending app, with KYC, a ledger and one payment provider | 12 to 16 weeks | $15,000 to $30,000 |
| Full platform | Several products, card issuing or open banking, fraud monitoring, admin console and web app | 5 to 9 months | $35,000 to $90,000 |
| Enterprise platform | Multi-market, core banking integration, custom ledger, high availability and audit-grade reporting | 9 months and up | From $90,000 |
Each market and licence type adds onboarding, reporting and audit work.
Banking-as-a-service partners cut months off the build; a custom ledger or core adds them.
Every payment rail, card issuer, KYC vendor and core system is its own project.
Native iOS and Android, a web app and the admin console are priced separately.
Every quote is fixed-price after a free scoping call. Provider fees, such as card issuing, KYC checks and payment processing, are billed by those providers and estimated up front.
Products we have shipped across digital health, streaming and voice AI, plus a solution showcase that connects voice calls to Odoo.
Paced breathing, a 21-day anxiety reset and night-time audio that keeps working on a bad connection.
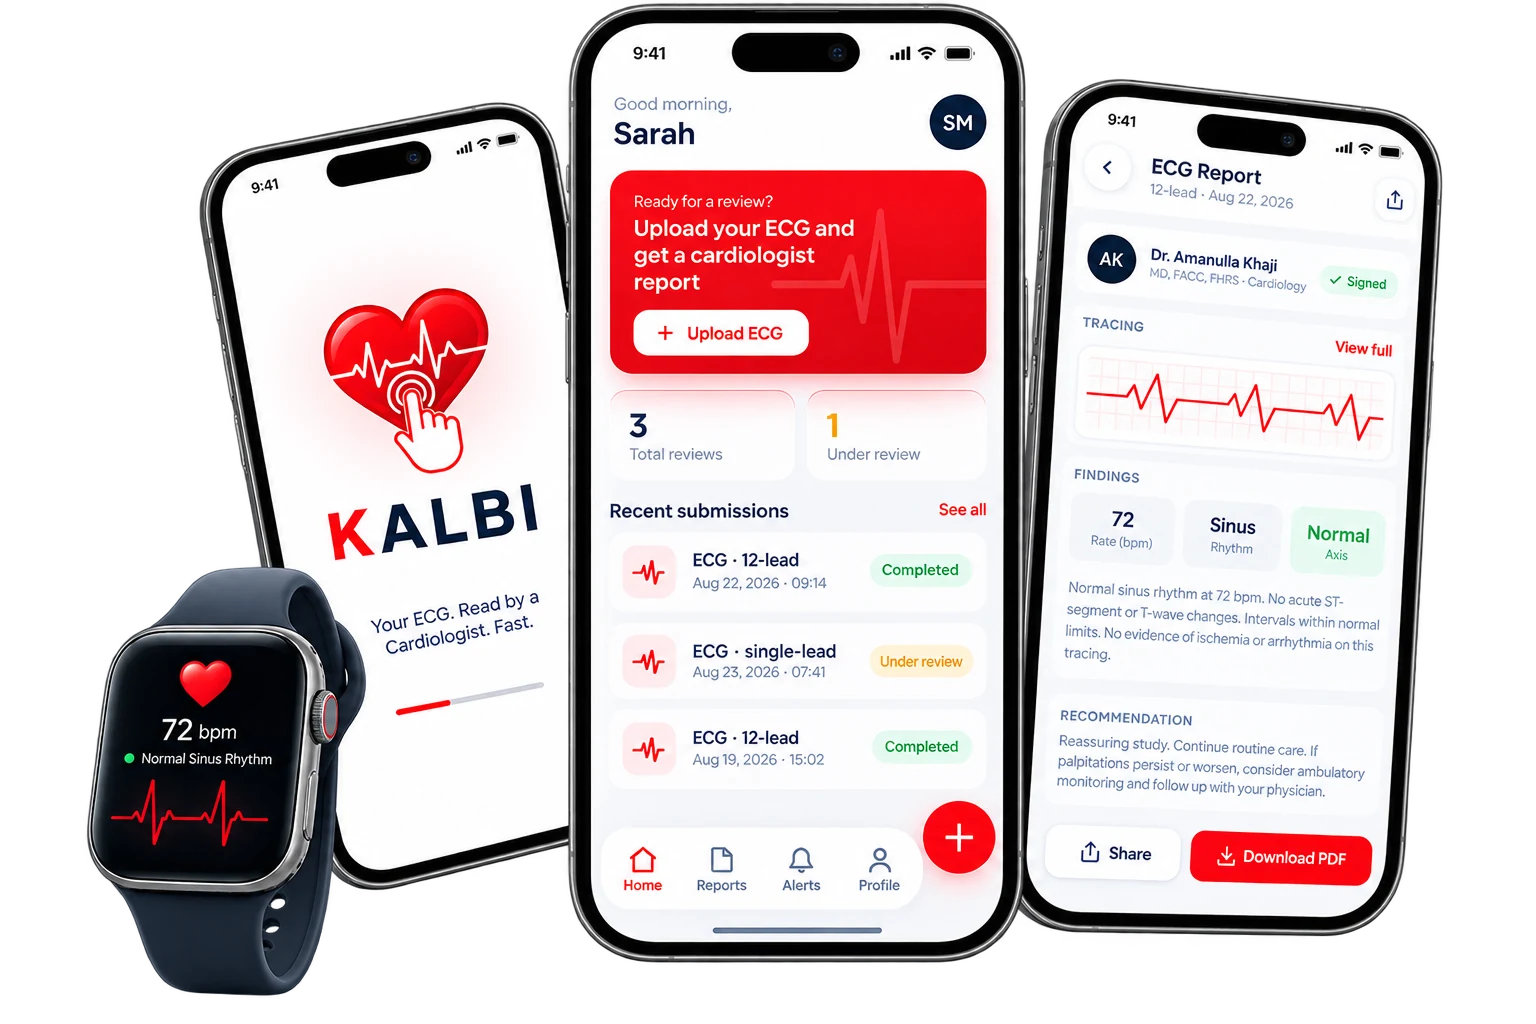
Patients upload an ECG from their phone and a cardiologist returns a signed report inside 24 hours.
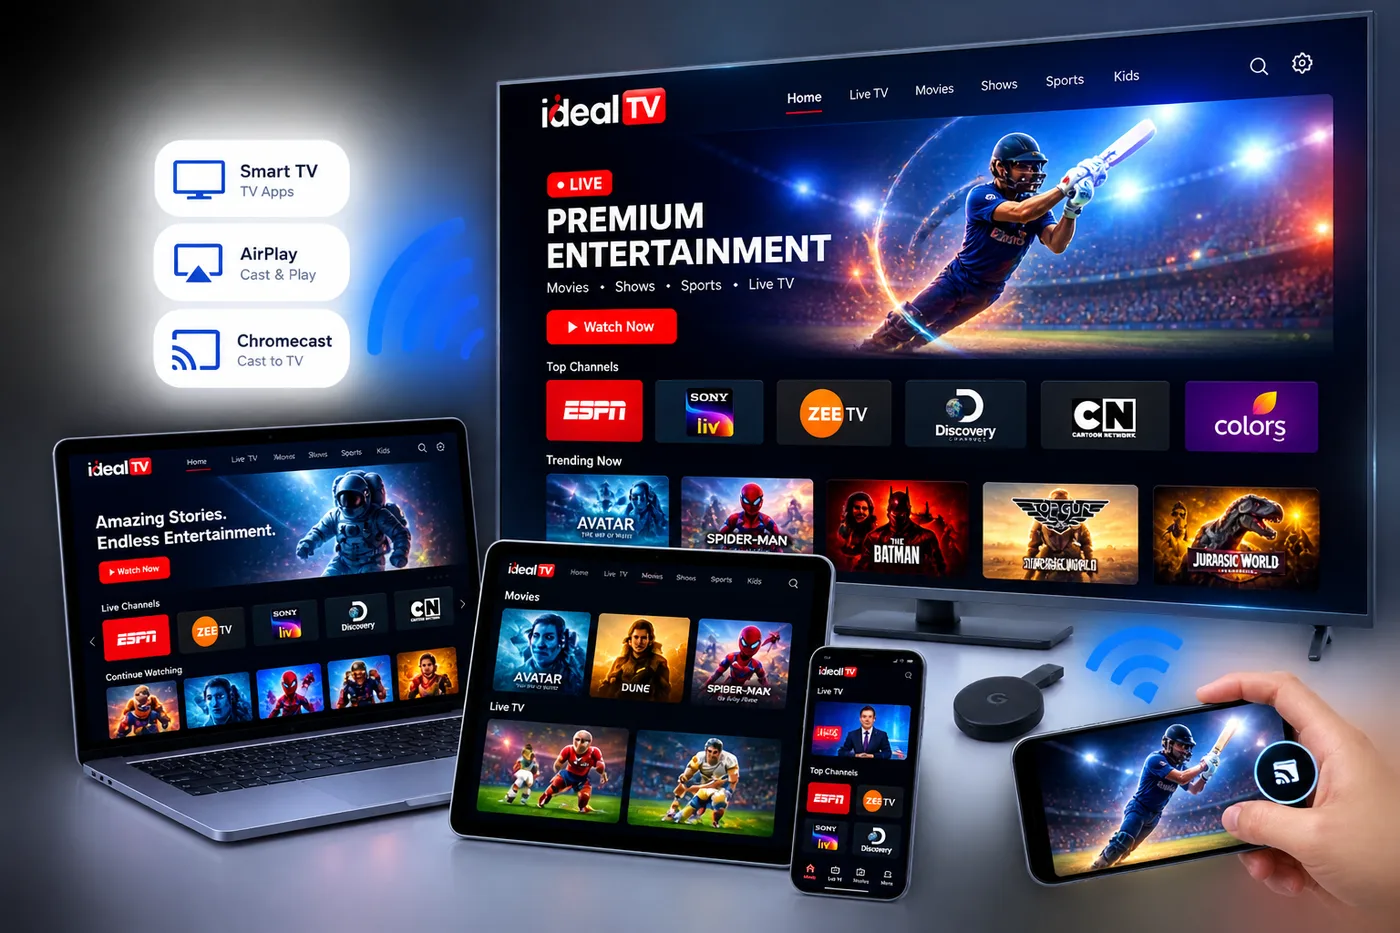
100+ live channels, movies and sport across mobile, web and connected TV, with one billing spine behind it.
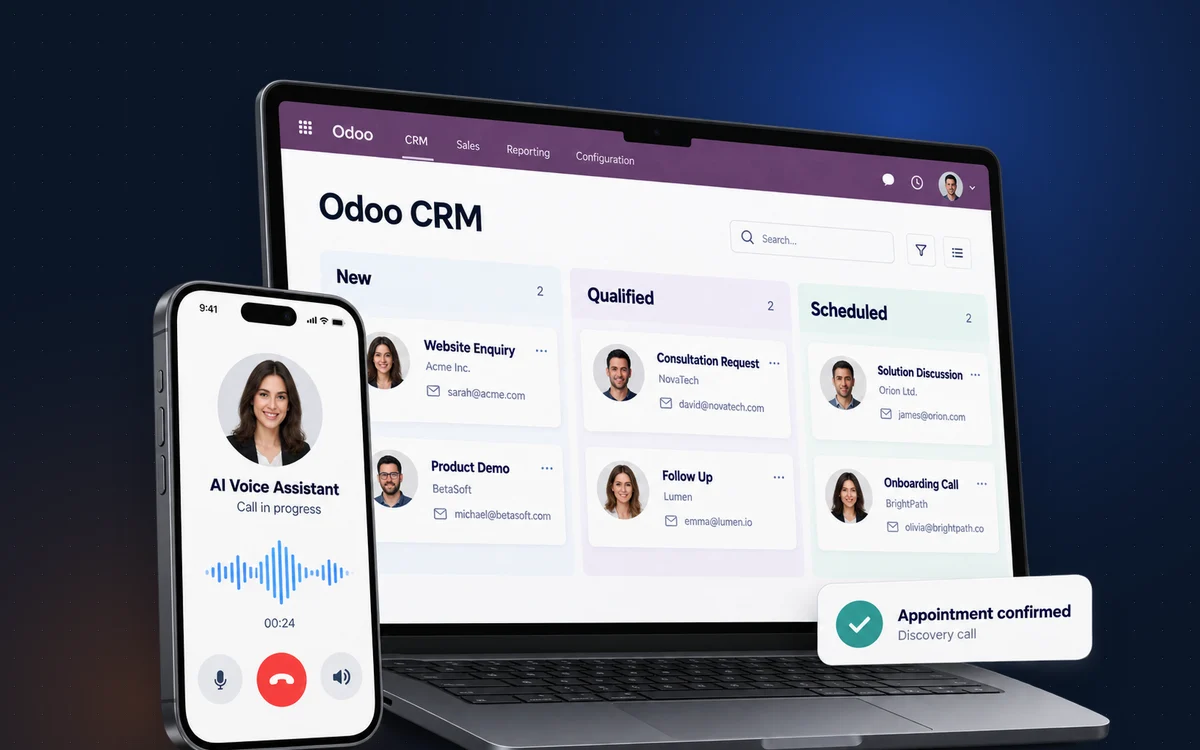
Voice calls connected to Odoo CRM and ERP: identity checks first, a verified order status read from the record, and a clear route to a person.
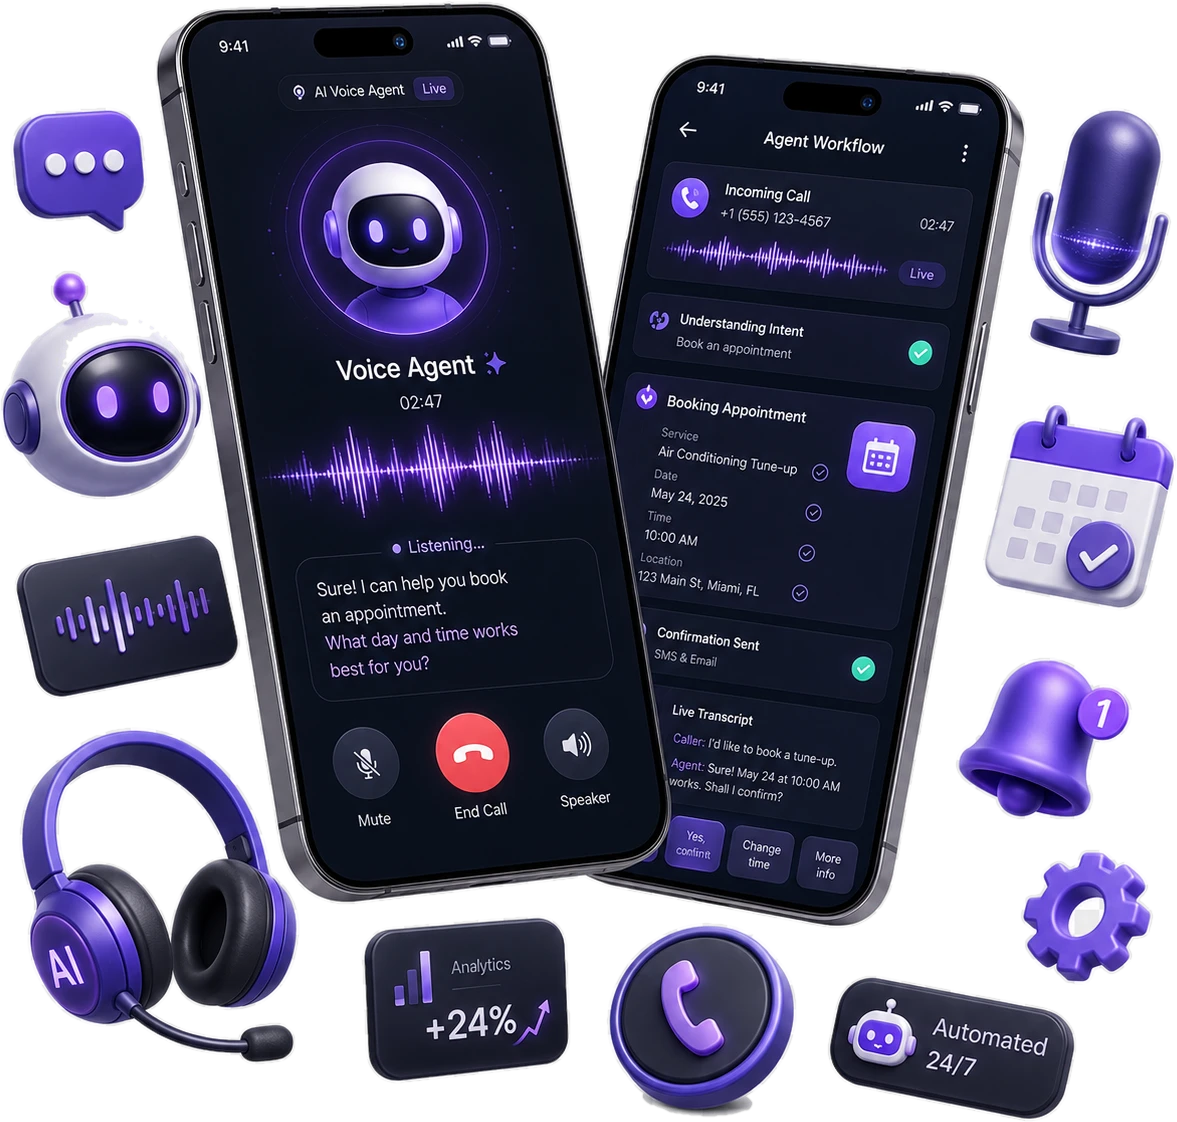
A HIPAA-ready voice agent that answers every patient call, books into the clinical system and hands over to a person when it should.
 Java
 Spring Boot
 Node.js
 Python
 React Native
 PostgreSQL
 Kafka
 Redis
 Stripe
Plaid
Onfido
 HashiCorp Vault
 Kubernetes
 AWS
 Temporal
Six financial segments with genuinely different compliance and architecture demands.
Neobanks and banking-as-a-service products.
Moving money quickly and reversibly.
Credit decisions and repayment lifecycles.
Investing products with market data obligations.
Quoting, binding and claims.
Remittance and multi-currency movement.
“Appther built our student competition app exactly the way we envisioned it: easy registration, smooth judging, and real-time results that keep participants engaged.”

“Building a mental health app means every detail has to be handled with care, and Appther got that from day one. The product feels warm, simple, and genuinely helpful.”
“Appther exceeded every expectation, on time and on budget, and the final product has been instrumental in scaling our business. A rare engineering partner.”

“Implementing an ERP across our operations felt daunting at first, but Appther made the transition seamless. Every department now works off a single source of truth.”
Field notes from real builds. No hype, just what worked and what didn't.
Wallets, lending and payments, with compliance, stack and MVP scope
How payment rail integration works, plus security and compliance costs
How banks automate customer service with NLP and local languages
Walk away from one call with a compliance scope, an architecture direction, a realistic budget range and a delivery timeline. No pitch deck, no obligation.
Keep exploring
Related services
Tell us what money movement you are enabling and in which markets. No sales pitch, just a straight answer on approach, scope, timeline and cost. Prefer email? Use our contact page.
Fields marked * are required. We reply within one business day.